Westminster Watch
- Seventh PM in a decade sworn in
- AI Regulation Bill clears final reading

 Politics
Landmark legislation prohibits smartphone sales to children under 16.
 Politics
Revolving door of British leadership since 2016 and what comes next.
 Business
Apple, Google, Meta face revenue hit from landmark UK legislation.
 Cyber
AetherOS detects threat pattern — here's what every business should know.
 Technology
What the new AI governance framework means for small business.
 Defence
Each political transition creates gaps in national cyber posture.
 Politics
Chancellor announces Midlands and Northern Powerhouse zones.
 Business
Despite political turbulence, small business optimism grows.
Politics
Landmark legislation prohibits smartphone sales to children under 16.
Politics
Revolving door of British leadership since 2016 and what comes next.
Business
Apple, Google, Meta face revenue hit from landmark UK legislation.
Cyber
AetherOS detects threat pattern — here's what every business should know.
Technology
What the new AI governance framework means for small business.
Defence
Each political transition creates gaps in national cyber posture.
Politics
Chancellor announces Midlands and Northern Powerhouse zones.
Business
Despite political turbulence, small business optimism grows.
Business
Despite political turbulence, small business optimism grows.
 AETHER PA
IDScan faces lawsuits over alleged sale of 153 million driver's licenses data breach.
Claude Mythos is a frontier AI model developed by Anthropic, purpose-built for deep code comprehension and system-level reasoning. It marks a deliberate shift away from general-purpose conversational models toward highly specialized, autonomous architecture.
What is Mythos? Mythos is a highly advanced AI capability developed by Anthropic that represents a massive leap in artificial intelligence. Moving beyond simply chatting or writing software, Mythos can act autonomously to find bugs in computer code, exploit those vulnerabilities, and execute cyberattacks across the entire "cyber kill chain." Its capabilities are described as being comparable to those of the National Security Agency (NSA). The Cybersecurity Impact A Double-Edged Sword: While Mythos is a potent offensive weapon, Anthropic is currently restricting its access to help secure critical infrastructure. It acts as a powerful defensive tool, effectively stress-testing new software to find and patch bugs much faster than human hackers. The "Messy Middle": Anthropic currently holds an estimated 6-to-8-month lead over adversaries and other AI labs. This creates a critical but difficult transition window where banks, energy providers, and governments must race to overhaul and patch their systems before bad actors gain access to similar autonomous hacking tools. Government Reliance and Tension The Capability Gap: The U.S. government is vastly behind the private sector in developing frontier AI models and must rely on companies like Anthropic for national security. Contracting Disputes: Despite depending on Anthropic to secure financial arteries and assist in active war zones, the Pentagon recently labeled the company a "supply chain risk" over a contract dispute. This has created a contradictory environment where the government is simultaneously relying on and fighting with its top AI provider. AI on the Battlefield (Project Maven) From Vision to Intelligence: Project Maven originally used AI to simply identify objects (like warships) in drone surveillance feeds to combat a shortage of human analysts. Accelerated Workflows: By integrating large language models like Anthropic's, the AI can now track enemy movements, note daily changes, and write the first drafts of intelligence reports. Unprecedented Scale: This technology allows the U.S. military to make tens of thousands of high-quality targeting decisions rapidly, scaling their capability from striking 50 targets a day to over 1,000 mobile or disguised targets within a 24-hour period.
Imagine discovering you've been paying hundreds of pounds every year for tools that now exist—for free. That moment has already arrived. A growing wave of Chinese AI platforms is disrupting the economics of artificial intelligence by offering capabilities once considered premium at little or no cost. The question isn't whether this trend continues. The question is whether subscription-based AI can survive it.
Open-source AI and free creative platforms are challenging the traditional subscription economy that has dominated generative artificial intelligence. As Chinese developers release increasingly capable models without recurring fees, businesses and creators face new opportunities and new strategic questions. This article analyses the emerging shift toward accessible AI and its potential impact on innovation, competition and the global creative economy. The rise of powerful, open-source, and free artificial intelligence platforms—largely driven by Chinese developers—is directly challenging the dominant subscription-based economic model of generative AI. Historically, accessing advanced AI capabilities required recurring financial commitments. However, the introduction of highly capable, zero-cost alternatives allows creators and businesses to access premium features without ongoing expenses, raising fundamental questions about the long-term viability of paid subscription models.
This shifting ecosystem presents both new opportunities and strategic challenges for users navigating the expanding availability of high-performing AI.
As cost-free platforms gain traction, the traditional AI market faces increasing disruption. Ultimately, the broader accessibility of these tools is expected to reshape market competition, influence global technological development, and alter the economic dynamics of the creative industry.
26 October 2026
A former pentester used the ARTEX AI pentesting framework to steal 8.2 million data records from various South Korean organizations. This operation involved seven suspects, and the stolen data included sensitive information that could be used for identity theft, financial fraud, and other malicious activities.
The use of ARTEX AI by a former pentester in this cybercrime operation underscores the evolving threat landscape that businesses face from sophisticated cyberattacks. ARTEX AI, designed to simulate human behavior and identify vulnerabilities, was apparently misused to exploit those vulnerabilities for malicious purposes. This incident highlights the critical importance of robust cybersecurity measures, including the ongoing monitoring and updating of AI tools to prevent their misuse. Furthermore, it emphasizes the need for continuous education and awareness within the SME community about the potential risks associated with AI tools. Small and medium-sized enterprises often underestimate the sophistication of cyber threats and the capabilities of AI, which can be easily misused. This analysis serves as a reminder that AI, whether for pentesting or other purposes, must be deployed with strict oversight and ethical considerations to prevent it from being utilized in illegal activities. The incident also points to the urgent need for stronger regulatory frameworks and stricter compliance measures. Without proper oversight, AI tools can be weaponized in ways that harm individuals and businesses. As such, it is crucial for regulatory bodies to work with technology providers to develop guidelines and standards that prevent AI from being misused. Lastly, businesses must prioritize their cybersecurity investments and consider implementing multi-layered defenses. This includes not only traditional cybersecurity measures but also advanced threat detection and response systems. By adopting a holistic approach to cybersecurity, SMEs can better protect themselves from such sophisticated cyberattacks that leverage AI. In the context of the UK SMEs, this analysis provides a clear imperative for them to enhance their cybersecurity practices to safeguard against such threats.
26 October 2026
The University of Copenhagen in Denmark revealed a data breach affecting personal information of 525,000 individuals, which included their names, dates of birth, and email addresses. This incident underscores the vulnerability of even the largest and most reputable institutions to cybersecurity threats.
The University of Copenhagen data breach is a stark reminder of the ever-present threat of cyber attacks, even for the most secure and well-funded organizations. This incident not only exposes a vulnerability in the institution’s cybersecurity protocols but also highlights the significant personal and financial risks posed to individuals whose data has been compromised. As the UK continues to evolve its regulatory environment around data privacy and protection, incidents like this serve as a powerful testament to the need for stringent data protection measures. For UK SMEs, this incident serves as a wake-up call. While larger institutions may have more resources to allocate to cybersecurity, smaller businesses often struggle to maintain robust security measures against sophisticated cyber threats. The University of Copenhagen's breach demonstrates that even a single vulnerability can be exploited to a significant extent, leading to a substantial data breach. As a result, UK SMEs must prioritize the implementation of advanced cybersecurity measures, including encryption, multi-factor authentication, and regular security audits, to mitigate risks and protect their customers' data. Furthermore, SMEs should consider investing in robust incident response plans to quickly address and mitigate the effects of a breach, ensuring that affected individuals are informed and support is available. By doing so, SMEs can safeguard their reputation and avoid potential legal and financial ramifications.
26 October 2026
China is launching a new state-owned enterprise to manage its vast data resources, aiming to fuel AI innovation and economic growth. This initiative, headquartered in Xiongan New Area, reflects Beijing's strategy to leverage its digital assets.
China’s ambitious bid to turn its abundant data into a competitive advantage in the AI race is a significant development for the nation, but its success hinges on overcoming the data-sharing barriers that have historically hindered digital innovation. As a state-owned enterprise, this group will play a pivotal role in ensuring data is accessible and utilized effectively across industries. This could lead to substantial advancements in AI technologies, from more personalized healthcare solutions to smarter urban planning. However, it also raises concerns about data privacy and the potential for misuse of sensitive information. The centralised approach may face challenges in balancing efficiency with the need for diverse and distributed data sources. For UK SMEs, embracing AI will become even more crucial, but they must also navigate the complexities of data access and security. Successfully navigating these issues will allow UK businesses to harness AI for competitive advantage, but they will also need to adapt to new regulatory landscapes and data protection standards.
11 October 2026
The Federal Bureau of Investigation arrested the co-founder of a cybersecurity firm in Canada, linking the arrest to an investigation into the ShinyHunters hacking group. The firm is suspected of stealing sensitive data on thousands of FBI agents.
The arrest of the co-founder of the ransomware negotiation firm by the Federal Bureau of Investigation highlights the ongoing challenges cybersecurity firms face in the digital espionage landscape. As the ransomware negotiation market grows, so too do the risks associated with dealing with such groups, particularly when they are suspected of stealing sensitive government information. This incident underscores the critical need for robust cybersecurity practices and regulatory oversight to prevent data breaches and protect sensitive information. For UK SMEs, this case serves as a reminder of the importance of comprehensive security measures, including encryption, secure data handling practices, and regular security audits. SMEs must also be vigilant and report any suspicious activities to the relevant authorities. Failure to protect sensitive data can lead to severe consequences, including legal liabilities and reputational damage. It is imperative for SMEs to work closely with cybersecurity experts to implement the necessary safeguards and stay informed about emerging threats.
11 October 2026
Japanese materials giant Sumitomo Bakelite is expanding its production of chip packaging materials in China and Singapore, following the second such announcement in the last four months. This expansion is driven by the increasing demand for more sophisticated semiconductors spurred by the AI boom.
As artificial intelligence (AI) continues to transform various sectors, including semiconductor manufacturing, the need for advanced chip packaging materials has surged. Japanese companies like Sumitomo Bakelite have recognized this trend and are adapting their production strategies to meet the growing demand. For UK small and medium-sized enterprises (SMEs), this expansion is significant as it suggests a broader global market for their products. SMEs in the UK, which often face challenges in scaling up production due to limited resources, might see this as an opportunity to expand their operations. However, they need to adapt their supply chains and production capabilities to compete in this new landscape. Sumitomo Bakelite’s decision to expand its operations in China and Singapore demonstrates its strategic foresight. It not only indicates a growing interest in AI-related technologies but also a recognition of the importance of a robust global supply chain. SMEs in the UK should consider leveraging such opportunities by enhancing their production capacities and exploring partnerships with established global manufacturers. This strategic move by Sumitomo Bakelite also highlights the importance of diversifying supply chains to mitigate risks and capitalize on emerging markets. The expansion of these companies into regions like China and Singapore underscores the growing global integration of the semiconductor supply chain. As a result, SMEs in the UK will have access to a larger pool of resources and a more diverse range of suppliers. However, they must navigate the complexities of international trade and production to successfully integrate into this expanding market. The trend towards AI and advanced chip packaging materials reflects a broader technological shift. SMEs in the UK need to stay informed and proactive to ensure they are not left behind in this rapidly evolving industry. By aligning their production strategies with these global trends, SMEs can position themselves for success in the future. Sumitomo Bakelite’s expansion is a testament to the potential opportunities and challenges that arise from technological advancements and globalization. SMEs in the UK should consider this as a catalyst for growth, embracing new technologies and strategies to remain competitive in the global market.
30 September 2026
US-based AI company Anthropic has raised concerns about Z.ai’s open-weight model GLM-5.3, highlighting its impressive hacking capabilities but also its weak safety measures. This poses a risk to UK SMEs, who may be targeted by cybercriminals using the model without adequate safeguards.
Anthropic’s warning about the potential misuse of Z.ai’s GLM-5.3 model is a stark reminder of the evolving threat landscape for small and medium-sized enterprises (SMEs) in the UK. The model, which almost matches the most advanced systems developed by Anthropic itself, demonstrates significant cyber capabilities that could be leveraged by malicious actors. However, it also highlights a critical vulnerability: the lack of robust safety protocols. This double-edged nature of the technology raises immediate concerns for SMEs, many of which rely on digital infrastructure for their operations and customer interactions. The lack of safeguards means that SMEs could become unwitting targets of cyberattacks, potentially leading to data breaches, financial losses, and reputational damage. It is crucial for SMEs to be aware of these risks and to implement robust cybersecurity measures to protect their digital assets. This includes not only the use of advanced AI tools but also continuous monitoring and updating of cybersecurity defenses to mitigate the impact of potential breaches. As the threat landscape continues to evolve, it is essential for SMEs to collaborate with cybersecurity experts and stay informed about the latest threats and best practices to safeguard their businesses from such sophisticated attacks.
26 September 2026
Hackers ShinyHunters exploited a path traversal vulnerability in the Grav CMS of Clop's leak site to gain unauthorized access and move the site to a new Tor address. This breach exposed sensitive information, demonstrating the importance of regular security patches and updates.
The recent breach of the Clop ransomware gang's leak site by ShinyHunters highlights a critical security flaw in the Grav CMS framework, specifically an unauthenticated path traversal vulnerability. This vulnerability exposes the potential for unauthorized access to web applications, which can lead to the theft or exposure of sensitive data. In the context of UK SMEs, this incident serves as a stark reminder of the vulnerabilities that can exist in software systems, particularly those not adequately protected by regular updates and security patches. For many small businesses, the Grav CMS and other open-source platforms might be used to manage their websites and web-based applications, making them prime targets for malicious actors. The lesson for SMEs is clear: it is imperative to stay vigilant and up-to-date with software maintenance. This means not only keeping applications and frameworks patched but also understanding the risks associated with using open-source tools and being aware of the latest security threats. Failure to address such vulnerabilities can lead to significant data breaches and financial losses, as experienced by Clop and ShinyHunters. Moreover, the incident underscores the importance of having robust cybersecurity measures in place. This includes implementing multi-layered security strategies, such as firewalls, intrusion detection systems, and regular security audits. SMEs should also consider employing professional cybersecurity firms to conduct thorough vulnerability assessments and to train their employees on basic cybersecurity practices. In the UK, where businesses are increasingly recognized for their contributions to the economy, the impact of such breaches can be particularly damaging. A single security breach can lead to the loss of customer trust, reputational damage, and potentially legal liabilities. Therefore, SMEs must prioritize not only protecting their own data but also that of their clients and partners. In summary, this incident serves as a powerful reminder of the importance of staying informed about software vulnerabilities and taking proactive steps to protect against them. For UK SMEs, the stakes are particularly high, and it is crucial to invest in robust cybersecurity measures to safeguard against such threats.
24 September 2026
Hackers are taking advantage of a critical vulnerability in Roundcube Webmail that was patched in May. This flaw allows for code injection attacks, a new threat that the Canadian Centre for Cyber Security is tracking.
The recent exploitation of the Roundcube Webmail vulnerability represents a significant cybersecurity concern for Small and Medium-sized Enterprises (SMEs) in the UK. With Roundcube being a widely used webmail service for SMEs, the attack not only compromises the confidentiality and integrity of the data but also poses a significant risk of financial loss, reputational damage, and potential regulatory penalties. For SMEs, this vulnerability highlights the need for robust, up-to-date security measures, including regular system updates and comprehensive security audits. Implementing advanced security protocols such as multi-factor authentication, encryption, and regular security training can help mitigate the risk of such exploitation. Furthermore, SMEs should consider implementing a robust incident response plan and maintaining a comprehensive backup strategy to protect against data loss. By prioritizing cybersecurity, SMEs can ensure they are not just surviving but thriving in a competitive marketplace where data breaches can have severe consequences.
23 September 2026
Cybersecurity firm Check Point has disclosed that its Security Gateway product is vulnerable to a remote code execution (RCE) flaw, which has been exploited by hackers. This flaw allows unauthorized access to certificate-handling features, posing a significant risk to UK SMEs.
Check Point's recent warning about the Security Gateway VPN RCE flaw is a stark reminder of the ever-present threat of cyberattacks targeting SMEs in the UK. This particular vulnerability, CVE-2026-85102, was actively exploited by malicious actors, indicating a real-world impact and the need for immediate action. For UK SMEs, this incident serves as a critical wake-up call, highlighting the importance of robust security practices and regular updates to protect against such vulnerabilities. Failing to address these flaws can lead to significant financial losses, reputational damage, and even business shutdowns due to data breaches. It underscores the necessity for SMEs to prioritize cybersecurity not just as an afterthought, but as a fundamental element of their business continuity and growth strategy. Implementing a comprehensive cybersecurity strategy, including regular vulnerability assessments and timely patching, can help mitigate the risks associated with this and similar vulnerabilities, ensuring that SMEs remain resilient against potential cyber threats.
19 September 2026
S&P Global Ratings suggests Asia-Pacific chip foundries are better prepared to weather a potential slowdown in artificial intelligence investment than other tech hardware firms in the region. The rating agency has stressed-tested four key sectors, finding foundries to be more insulated.
As the market grapples with concerns over slowing Big Tech spending and calls for a more cautious approach to frontier artificial intelligence, chip foundries in the Asia-Pacific region have emerged as a more resilient sector. This assessment by S&P Global Ratings underscores the strategic importance of foundries in the broader tech ecosystem, particularly for the development of AI technologies that are crucial for innovation in various industries. The resilience of foundries in this context highlights the critical role they play in the supply chain for AI development. As AI technologies evolve, they demand advanced processing capabilities and specialized equipment, which foundries are ideally positioned to supply. Foundries have invested significantly in developing the next-generation semiconductor technologies that are essential for AI applications. Additionally, they are better equipped to manage the complex supply chain challenges that come with these technologies, ensuring a steady and reliable flow of components. In contrast, other sectors such as memory manufacturers and cooling component suppliers might find their investment in AI applications more vulnerable to market shifts. This is because memory manufacturers often focus on general-purpose memory chips, which are less directly tied to AI applications. Similarly, cooling component suppliers, while important for maintaining the performance of AI systems, are not as specialized in AI technologies themselves. The findings by S&P Global Ratings are particularly relevant for UK SMEs, which often operate in a highly competitive and technology-driven environment. For SMEs in sectors that rely heavily on AI, such as manufacturing, healthcare, and finance, understanding the potential risks and opportunities in the AI market is crucial. SMEs in these sectors need to ensure they are well-positioned to take advantage of the AI-driven opportunities while also managing the risks associated with market shifts and potential downturns in AI investment. By positioning itself as a leader in AI-chip development, the foundry sector can act as a strategic partner for SMEs across various industries. Foundries can provide the necessary technologies and components to support AI innovation, thereby enabling SMEs to stay competitive and adapt to the evolving landscape of artificial intelligence. However, SMEs must also be aware of the potential challenges and invest in strategies to mitigate risks and capitalize on opportunities as they arise.
19 September 2026
Gyazo, an image-sharing platform, experienced a data breach following a server vulnerability that exposed 23.6 million user records. This breach highlights a critical weakness in the platform's security measures.
The data breach at Gyazo, which exposed 23.6 million user records, is a severe setback for the UK's SMEs, particularly those utilizing the platform for business purposes. For SMEs, the loss of such sensitive information can have far-reaching implications, including financial losses, reputational damage, and compliance issues. The exposure of such a large number of records could compromise personal and sensitive data, leading to potential identity theft, financial fraud, and legal liabilities. For SMEs in the UK, the importance of data security cannot be overstated. This incident serves as a stark reminder of the critical nature of protecting user data, especially when dealing with personal information. SMEs need to be more vigilant in their cybersecurity measures and ensure they are using robust and regularly updated security solutions. They should also consider implementing comprehensive data breach response plans to minimize the impact of such breaches. Failing to do so can lead to significant financial and reputational damage, which can severely impact a business's ability to operate effectively and grow. In the context of the UK, with its stringent data protection laws, such as the GDPR, the exposure of personal data can result in substantial fines and legal action. Therefore, it is crucial for SMEs to prioritize security and invest in advanced security technologies to protect their users and their sensitive data.
16 September 2026
Cybersecurity agencies in the US, UK, and the Netherlands have exposed a Windows malware developed by Iran's intelligence service. This malware can copy emails and chat messages, take screenshots, and activate microphones to record conversations, all controlled via Telegram.
The recent revelation of Iran's espionage malware targeting dissidents, journalists, and activists through Telegram-controlled Windows malware is a concerning development for cybersecurity in the UK and globally. This malware represents a sophisticated and covert method of surveillance, underscoring the ongoing threat posed by state-sponsored cyber espionage. For UK small and medium enterprises (SMEs), this poses significant risks, as the malware's capabilities could enable unauthorized access to sensitive communications and data. SMEs, often without robust cybersecurity measures, are particularly vulnerable to such threats. The exposure of this malware highlights the necessity for enhanced cybersecurity measures and awareness among SMEs. Implementing strong encryption, regular security audits, and training employees on recognizing and preventing cyber threats are crucial steps. SMEs should also consider using multi-factor authentication, secure backups, and secure communication channels to protect sensitive information. Additionally, they should be vigilant about phishing attempts and suspicious communications, which can often be the first step in an attack chain. By proactively fortifying their cybersecurity defenses, SMEs can better protect themselves from these sophisticated espionage efforts.
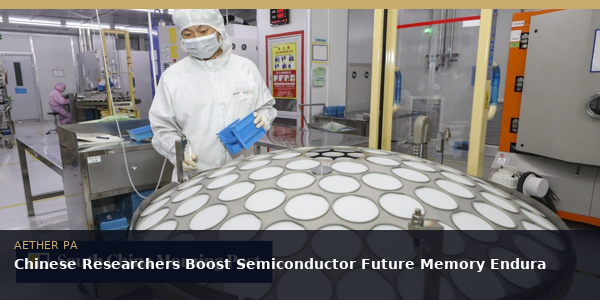
14 September 2026
Chinese researchers have improved the endurance of a type of future memory chip, which can switch between two electric states to store data. This development could significantly enhance the reliability of these chips, which are crucial for high-performance computing and advanced AI systems.
The development by Chinese researchers in extending the endurance of semiconductor memory chips represents a significant advancement in the technology of future memory. This breakthrough is crucial for the future of artificial intelligence and high-performance computing, as it addresses a long-standing reliability barrier. In the UK, where SMEs are increasingly looking to incorporate AI and advanced computing technologies into their operations, this advancement promises substantial benefits. One of the key areas of focus for SMEs in the UK is the integration of AI and advanced computing technologies, which can drive efficiency and innovation. The endurance enhancement in this type of memory chip could enable more reliable and longer-lasting AI systems and computing platforms, which are essential for SMEs looking to leverage these technologies. This development suggests that UK businesses can expect more robust AI systems and computing solutions, potentially reducing the risks associated with data reliability and providing a competitive edge. The improvement in endurance not only enhances the performance and stability of AI systems but also opens up new possibilities for the use of these chips in various industries, including healthcare, finance, and manufacturing. As the AI market continues to grow, SMEs in the UK will need to be prepared to invest in and adopt these advanced technologies. By incorporating these enhanced memory chips, UK SMEs can better position themselves to take advantage of the AI boom and improve their operational efficiency. Furthermore, the long-term impact of this advancement extends beyond the immediate benefits of AI and computing. The stability of these chips could lead to more consistent and reliable data storage, which is crucial for the secure and efficient operation of AI systems. This could help SMEs in the UK to build trust in their AI investments, which is essential for the wider adoption of these technologies. Ultimately, the durability of these memory chips could lead to a more stable and predictable AI ecosystem, which is vital for the UK’s broader technological and economic growth.
13 September 2026
Beijing and domestic Chinese tech firms are working to integrate AI into chip design software to strengthen national self-sufficiency. Empyrean Technology, the country's leading electronic design automation company, has been using AI-optimized algorithms and tools to accelerate the chip design process, according to chairman Liu Weiping.
As Beijing pushes forward with AI-assisted chip design, the implications for UK SMEs are significant. The integration of artificial intelligence into chip design software is a strategic move towards achieving self-sufficiency in high-tech manufacturing sectors. For UK SMEs, this shift could represent both challenges and opportunities. On one hand, SMEs might face increased pressure to adopt similar AI technologies to remain competitive and avoid being left behind in a rapidly evolving technological landscape. On the other hand, SMEs could potentially gain access to advanced design tools and processes, enabling them to innovate and develop cutting-edge products more efficiently. Moreover, this trend highlights the importance of developing strong AI capabilities within domestic industries. In the UK, SMEs may need to accelerate their AI investments and collaborations with tech giants or startups to maintain their competitive edge. However, the UK's SME sector
11 September 2026
AI experts are expressing alarm over safety concerns ahead of the Xi-Trump summit in Washington, with cybersecurity breaches and declining model safety visibility leading to calls for a slowdown in US artificial intelligence development. These concerns come at a time when the summit will focus on high stakes and technological lead.
The mounting concerns over AI safety and development, as highlighted by the recent cybersecurity breaches and declining visibility into model safety, have the potential to significantly impact the upcoming Xi-Trump summit. This development is particularly significant as the leaders from China and the United States will be meeting to address crucial issues ranging from trade to technological dominance. The recent events, including the internal whistle-blowing and the broader safety risks, suggest that the US artificial intelligence (AI) boom is facing significant challenges. These challenges are not only technical but also geopolitical, as they could shape the global landscape of AI technology and innovation. The AI industry, which has seen rapid growth and development, is now at a critical juncture where the safety of the models and the broader ecosystem need to be addressed. This is crucial as it will determine how the technology evolves and the impact it has on society and economies around the
09 September 2026
Researchers in the US have shown how artificial intelligence can be used to hijack WeChat accounts through voice calls, drawing attention to the growing threat of AI-driven cyber threats and prompting calls for cooperation between the US and China.
The recent revelation that artificial intelligence has been used to exploit vulnerabilities in WeChat, a popular messaging and payments platform used by millions, serves as a stark reminder of the evolving landscape of cyber threats. This incident underscores the potential for AI to be weaponized in ways previously unimaginable, making it essential for nations to collaborate and share intelligence to mitigate such risks. In the case of WeChat, it appears the US researchers identified a flaw in the app and then developed a tool (WeWorm) to exploit it, highlighting the rapid development of AI capabilities. This incident not only highlights the technological prowess of the US in cybersecurity but also the necessity for international cooperation in cybersecurity. As technology advances, the boundaries between different countries become more porous, and the risks of cyber attacks from one nation crossing borders increase. The United States and China, two of the world's largest economies, have a particular interest in cybersecurity,
09 September 2026
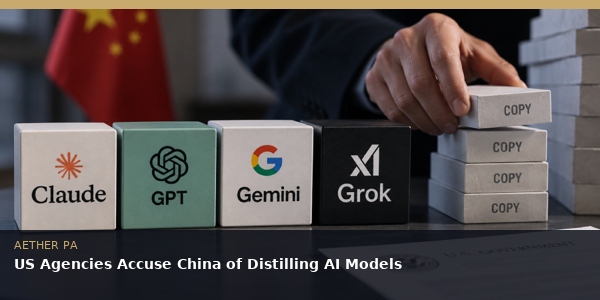
The U.S. agencies have accused Chinese AI firms of conducting systematic extraction of proprietary functionalities and capabilities from American AI models, such as Claude, GPT, Gemini, and Grok. This activity is said to be an integral part of China's AI development strategy.
The accusation from the U.S. agencies highlights a concerning trend in the global AI ecosystem. China's approach to AI innovation appears to be heavily reliant on unauthorized access to sophisticated American models, which, when combined with China's industrial-scale efforts, poses a significant threat to the proprietary and competitive edge of American enterprises, particularly Small and Medium-sized Enterprises (SMEs). In the UK, SMEs are the backbone of the economy and innovation. They often struggle to match the financial resources and technological capabilities of their larger competitors. This situation could severely impact SMEs' ability to innovate and maintain a competitive edge in the AI landscape. The act of distillation, in which companies extract specific functionalities or entire models from existing systems, represents a sophisticated form of industrial espionage. It enables AI developers in China to rapidly improve their models without having to invest in the research and development necessary to create them
08 September 2026
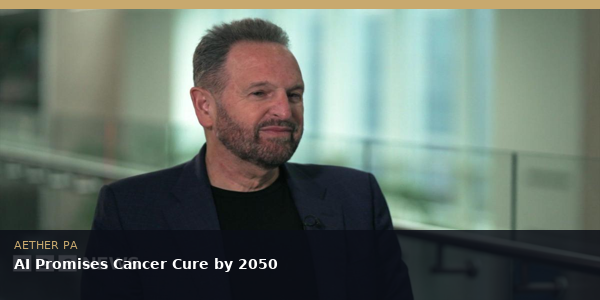
René Haas, the chief executive of Arm Holdings, predicts that artificial intelligence will find a cure for cancer within the next few decades. His comments were featured on BBC Business, where he stated that AI will achieve what "scientists have dreamed of for decades."
René Haas’s optimistic stance on AI’s potential to cure cancer by the early to mid-21st century is a bold claim that carries significant implications for the UK’s SME sector. If such predictions were to materialize, they would have a profound impact on both the pharmaceutical and AI industries. The successful implementation of AI could lead to more personalized and targeted treatments, potentially reducing the cost and complexity of cancer research and development. For SMEs in the UK, particularly those focused on pharmaceuticals and healthcare technologies, this could mean a competitive edge as they integrate AI solutions into their core business models. However, the implementation of AI in cancer treatment is not without its challenges. Regulatory frameworks, ethical concerns, and the need for robust data security systems will all play crucial roles in ensuring that AI is developed and utilized responsibly. SMEs will need to stay abreast of these
08 September 2026
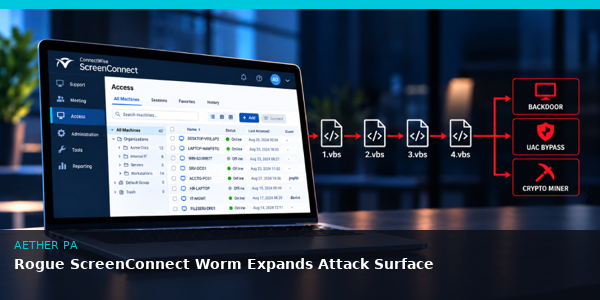
Cybersecurity researchers have identified a worm-like pattern of activity that leverages ConnectWise ScreenConnect to distribute a malicious Visual Basic Script payload to new systems. Three different initial access methods were used in three separate incidents, highlighting the need for enhanced security measures.
Rogue ScreenConnect clients have demonstrated a sophisticated and adaptable approach to cyber attack, expanding the attack surface for UK SMEs through a combination of varied initial access vectors. This new threat underscores the critical need for comprehensive security protocols, including robust endpoint protection, regular system updates, and employee cybersecurity training. SMEs must prioritize these measures to protect their networks and data from persistent and evolving threats. Failure to address these vulnerabilities could result in significant financial losses, reputational damage, and potential legal liabilities. By adopting stringent security practices, SMEs can mitigate the risk of such attacks and ensure a more secure digital environment.
07 September 2026
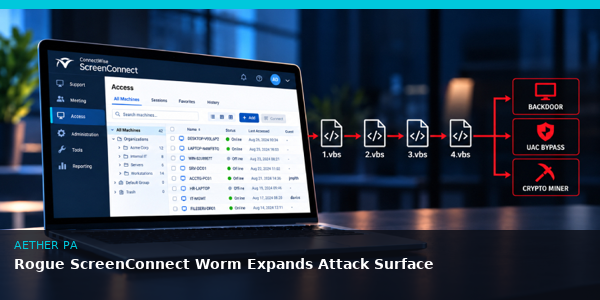
Cybersecurity experts have uncovered a worm-like behavior that leverages ConnectWise ScreenConnect to deliver a malicious VBScript payload to new systems. Three distinct initial access methods—tech-support scams, phishing, and fake software—have been identified as the vectors for these incidents.
The recent revelations from Huntress highlight a concerning trend in cybersecurity where rogue software, specifically using ConnectWise ScreenConnect, has been deployed to spread malicious Visual Basic Script across newly connected systems. This activity poses a significant threat to UK SMEs, as these organizations often rely on technology tools like ScreenConnect for remote assistance and support. The ease with which such a worm-like behavior can propagate underscores the need for robust security measures that go beyond simply blocking known bad actors. SMEs must prioritize continuous monitoring and adaptive security protocols to detect and mitigate threats like this one. Additionally, training employees on recognizing phishing and tech-support scams is crucial, as these are often the initial access points for attackers. By understanding and addressing the vulnerabilities created by these initial access methods, SMEs can better protect themselves against the broader threat landscape. Implementing multi-factor authentication, endpoint detection and response (EDR) systems
07 September 2026
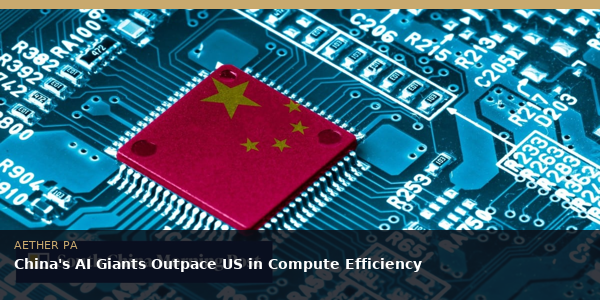
A Moody’s Ratings report reveals that despite spending significantly more on AI, US tech giants still fall behind in terms of computing power per dollar when compared to their Chinese counterparts. This suggests that domestic subsidies and government support in China contribute to greater efficiency in AI investment.
The report from Moody’s Ratings highlights a stark contrast in the efficiency of artificial intelligence spending between the US and China. Despite the US tech giants outspending their Chinese counterparts, the physical advantage in terms of computing power per dollar is not as pronounced as one might expect based on their spending. This efficiency advantage is attributed to several factors, including lower domestic costs and substantial state support in China. For UK SMEs, this analysis is particularly relevant as it underscores the importance of computational efficiency in AI investments. As UK businesses increasingly adopt AI technologies, understanding and replicating China’s strategy could provide a competitive edge. By prioritizing efficiency in AI spending, UK SMEs can maximize the benefits of their investments, ensuring that each dollar spent on AI yields the maximum possible return. This efficiency advantage not only saves costs but also enhances the effectiveness of AI applications, potentially leading to better decision-making and innovation
07 September 2026
IDScan, an identity verification company, has been sued over an alleged data breach that exposed the personal information of over 153 million drivers. The lawsuits accuse the company of hacking their system and selling sensitive data online.
The IDScan data breach affecting over 153 million drivers is a significant and concerning development for UK SMEs, particularly in the automotive and insurance sectors. This incident highlights the critical importance of robust cybersecurity measures to protect sensitive personal and financial data. For SMEs reliant on driver's license information, such as insurance companies and rental car services, the breach could lead to increased fraud and increased costs to verify customer information. This not only puts these businesses at risk but also endangers consumer trust and compliance with data protection regulations like GDPR. Furthermore, the fact that this data has been sold online suggests a potential security failure in the way IDScan handled and protected customer information. This breach could expose not only personal data but also potentially financial information, such as credit card details, making it even more serious. For UK SMEs, this incident serves as a stark reminder of the necessity of investing in advanced cybersecurity solutions and compliance with
 Featured
Legislation passed through Parliament this week officially bans the sale of smartphones to anyone under 16. Social media platforms must now enforce strict age verification or face fines of up to 4% of global turnover. Apple, Google, and Meta shares dipped sharply following the announcement.
 Politics
As we mark another resignation, an entire generation has now lived through seven different occupants of No10. Each one came with big promises and bold plans — few delivered lasting change. Here's our deep dive into what this means for policy stability and SME planning.
 Politics
Each leadership transition creates gaps in cyber posture, policy continuity, and regulatory focus. Our analysis shows a direct correlation between political instability and increased vulnerability windows for UK businesses.
 Cyber Security
A coordinated ransomware attempt across three NHS trusts was neutralised early after AetherOS heuristic nodes flagged the anomalous pattern. Full incident report now available through our threat intelligence dashboard.
 Business Global
Market analysts suggest the phone ban could accelerate the shift towards AI-powered platforms that don't rely on traditional app-store dynamics. Smaller tech firms may benefit from reduced competition for younger demographics' attention.
 Technology
The newly passed legislation creates a tiered system for AI regulation, with exemptions for companies under 50 employees. AetherOS compliance tools can help you navigate the requirements with minimal overhead.
 Defence
As international negotiations stall over cryptographic key custody, UK firms must prepare for potential data localization requirements. Our guide outlines the practical steps to ensure compliance.


27 October 2026 - Aether P.A.
Labour Party has unveiled a £285 million funding boost to support local communities, empowering mayors to make decisions closer to home and reducing reliance on Westminster.
This move matters to UK communities by enhancing local governance and decision-making power, crucial for addressing regional needs and priorities.
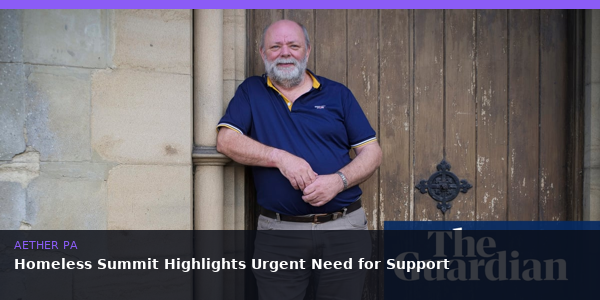
27 October 2026 - Aether P.A.
Andy Burnham's summit on rough sleepers highlights frustration with bureaucratic barriers and a critical need for immediate support. Martin Fletcher's success shows that a supportive approach is key, moving beyond forms and judgments.
This summit matters to UK communities and SMEs as it underscores the urgent need to streamline support systems and provide compassionate care for those in need.
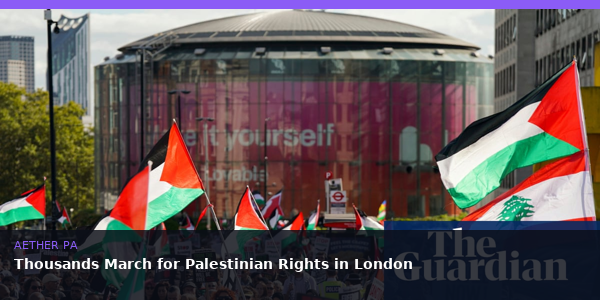
11 October 2026 - Aether P.A.
Thousands gathered in central London to protest against Israeli occupation, marking three years of violence and calling for an end to “genocide.”
This matters to UK communities and SMEs as the conflict directly impacts global trade and relations, affecting investments and business opportunities in the region.
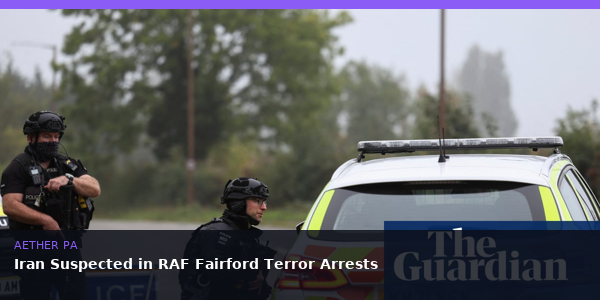
30 September 2026 - Aether P.A.
Labour's Andy Burnham asserts strong evidence Iran was involved in the recent terror arrest near RAF Fairford, as five men were detained.
UK communities and SMEs must remain vigilant as tensions rise between Iran and the West.
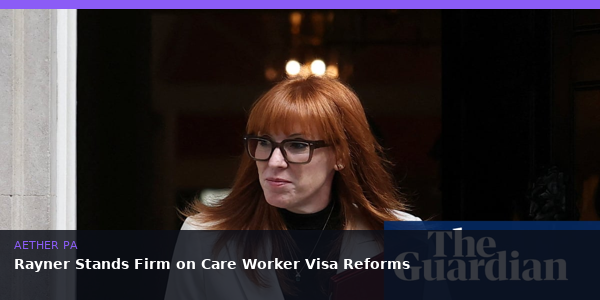
26 September 2026 - Aether P.A.
Housing Secretary Angela Rayner defended the Labour Party's position on new visa rules that would make it harder for foreign care workers to get permanent residence in the UK.
UK communities and SMEs stand to lose as Rayner argues that these changes threaten the availability of skilled foreign workers in the healthcare sector.
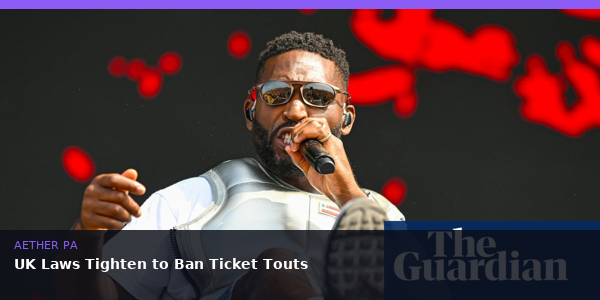
26 September 2026 - Aether P.A.
UK lawmakers are intensifying efforts to ban profit-driven ticket resellers, following high-profile requests from artists like Tinie Tempah and Mike Joyce of The Smiths. Prime Minister Keir Starmer promised to crack down on fans being fleeced by sites like Viagogo and StubHub.
This matters to UK communities and SMEs, as fans and businesses face potential financial losses, and the government aims to protect consumers from unfair practices.
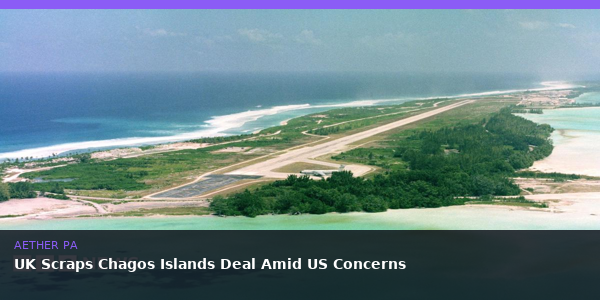
23 September 2026 - Aether P.A.
Defence Secretary Wes Streeting confirms a review of the Chagos Islands deal following President Trump's criticism of Andy Burnham.
The UK's decision underscores the importance of diplomatic relations in international agreements.
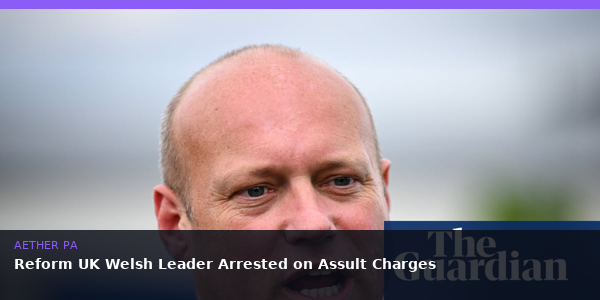
15 September 2026 - Aether P.A.
Dan Thomas, elected leader of Reform UK in Wales, has been arrested and bailed on suspicion of assault and controlling behavior. His resignation follows rapidly, as he seeks to avoid being a distraction for Reform UK's May election.
This matters as the arrest could impact Reform UK's strategy and credibility ahead of the May election, potentially undermining support from Welsh voters.
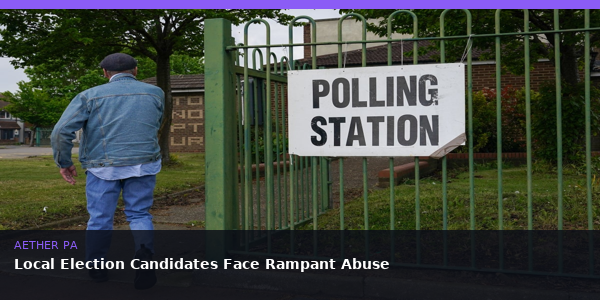
14 September 2026 - Aether P.A.
In 2026, nearly two-thirds of local election candidates reported encountering intimidation and abuse during their campaigns, highlighting a concerning trend in democratic discourse.
This issue matters to UK communities and SMEs as it undermines fair participation in elections and fosters a hostile environment for future candidates.
14 September 2026 - Aether P.A.
Police have released images of six men involved in an anti-migrant protest in Portsmouth last week, following incidents where officers were injured and vehicles were damaged.
The release of images highlights the escalating tensions between anti-migrant protesters and law enforcement in Portsmouth, a matter of growing concern for local communities and small businesses.
"Aether mapped our entire operational structure in two weeks. We found £40K in hidden inefficiencies and our audit prep went from 6 weeks to 4 days."
— UK Manufacturing SME, 2025AETHER News OS is an AI-powered intelligence operating system designed to transform thousands of global news articles into actionable business and strategic intelligence. Rather than functioning as a traditional news reader, it continuously collects, analyses, categorises, and scores information to identify emerging risks, opportunities and significant events across multiple sectors.
The platform uses intelligent scoring models to assess cyber threats, geopolitical developments, defence activity, economic change, technology breakthroughs and business impact. Every story is ranked, scored and prioritised through AI to deliver meaningful intelligence instead of information overload.
Designed for business leaders, cybersecurity professionals, SMEs and decision-makers, AETHER News OS provides a live intelligence command centre that helps organisations understand what matters most, why it matters and how it could affect operations.
Every claim tested. Every forecast original.
A personalised feed built around what you need.
Command Centre — Live Operational Exposure
Confirms the intelligence pipeline is live and actively scanning sources.
Aggregate risk rating calculated from today's highest-scoring intelligence.
How confident the scoring model is in today's threat assessment.
The single highest-scoring item in today's feed — your top priority read.
Ranked by total intelligence score, scaled to the top sector
Share of total intelligence volume
How concentrated risk is across sectors today.
The sector generating the most intelligence volume.
Number of distinct sectors represented in today's feed.
Mean intelligence score across all monitored sectors.
Today's top story intelligence score.
Score recorded in the last update cycle.
Direction of change between the two readings.
Regional threat exposure — powered by AETHER geo-analytics